Audit & Assurance · Srida IT’s primary practice
Independent assurance that your controls actually work.
Srida IT is an Audit & Assurance-led firm. We deliver independent, evidence-based assessments across cybersecurity, IT, ISO, SOC, AI governance, privacy, cloud and resilience — product-accelerated, continuously assured, and delivered internationally on a project basis (remotely and on site where required). Formal certification, attestation and locally-authorised assessments are provided via accredited bodies and partners.
Evidence-based
We corroborate every finding against configuration, logs and artefacts — we verify, we don't assume.
Independent by design
Assurance is delivered separately from advisory and implementation, so objectivity is never compromised.
Continuously assured
Point-in-time assessment, then ongoing control monitoring — so you stay in control between audits.
Audit & Assurance services
One portfolio. Every control domain.
Cybersecurity & Information Security Assurance
AvailableEvidence-based assessment of how well your security actually holds up.
Learn more →IT Audit, ITGC & SOX Readiness
AvailableGet your IT general controls audit-ready — before the auditors arrive.
Learn more →ISO Management System Internal Audits
AvailableInternal audits that keep your ISO management system certification-ready.
Learn more →SOC 1 / SOC 2 Readiness
AvailableBe ready for your SOC examination — before the CPA firm starts.
Learn more →AI Governance & AI Security Assurance
AvailableGovern, secure and evidence your AI — before it governs you.
Learn more →Privacy & Data Protection Assessments
DPDPA and GDPR readiness, privacy governance, data mapping and control testing.
Learn more →Cloud & Third-Party Assurance
AvailableAssurance over the cloud you run on and the vendors you depend on.
Learn more →ESG & Sustainability Readiness
On requestAn emerging, scoped engagement — ESG reporting readiness and controls review.
Learn more →Continuous Assurance & Control Monitoring
Ongoing visibility of control health, evidence freshness and risk movement between audits.
Learn more →RBI Cyber Resilience for Payment Operators
Readiness, remediation and independent assurance against the RBI Master Directions for non-bank PSOs (2026).
Learn more →Business Continuity & Operational Resilience
On requestBe ready to keep running when something goes wrong.
Learn more →OT / Industrial Cybersecurity Assurance
On requestSecure the systems that run the physical world — safely.
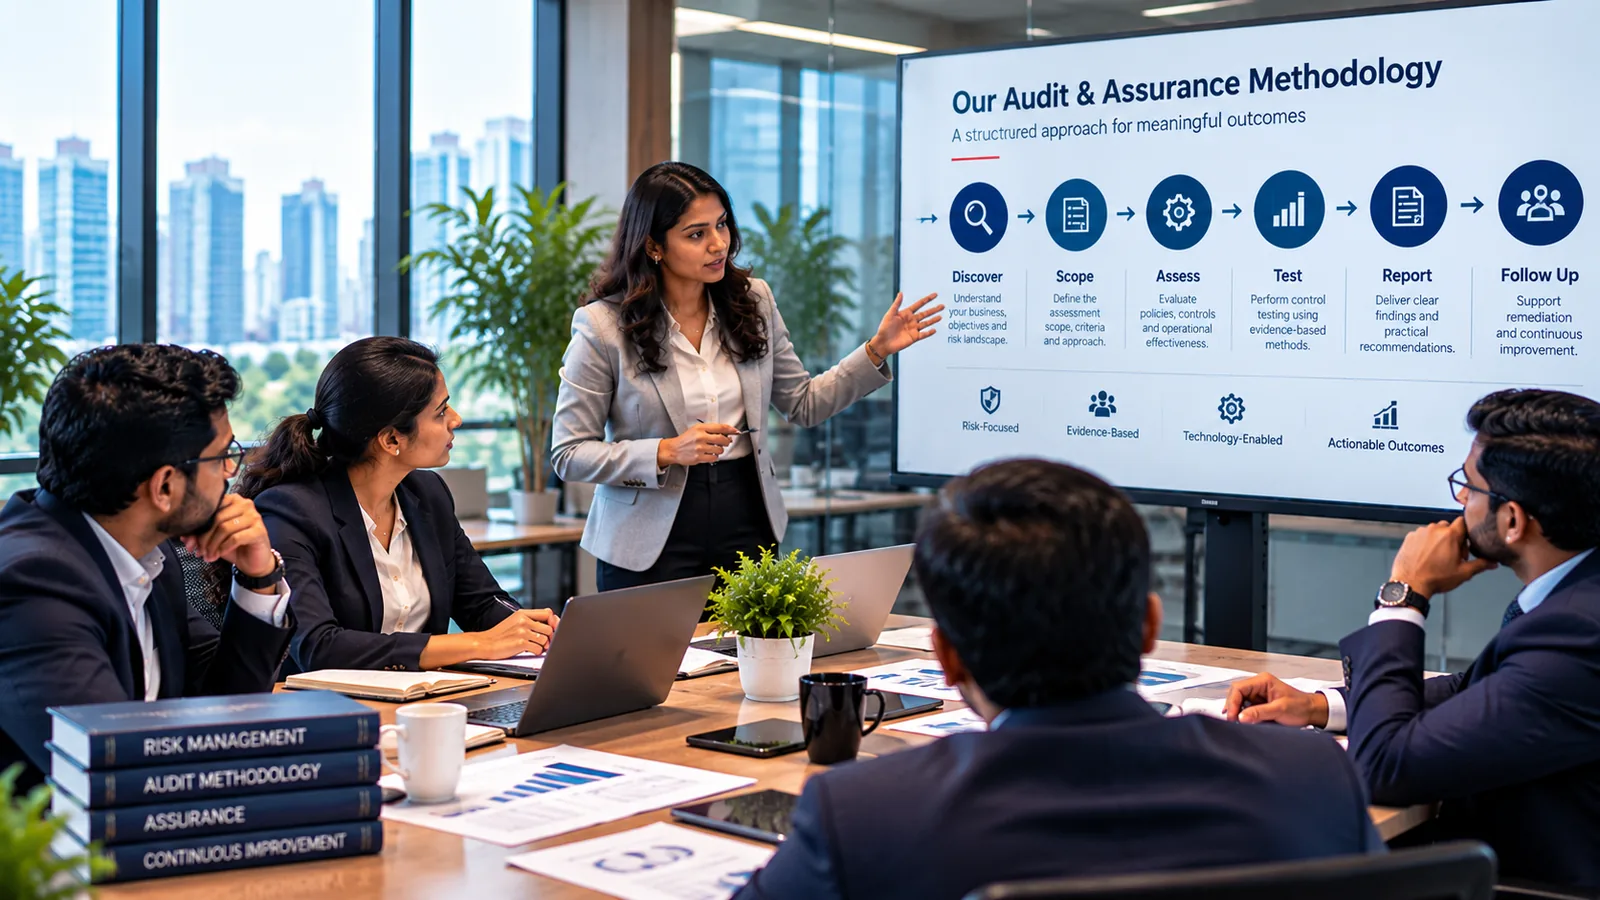
Learn more →Our methodology
How every engagement runs.
01
Discover
Understand your business, technology, regulatory drivers and threat landscape.
02
Scope
Agree the control domains, systems and evidence in scope, and the assessment plan.
03
Assess
Review control design through documentation, interviews and walkthroughs.
04
Test
Test operating effectiveness against evidence — we corroborate, not assume.
05
Report
Risk-rate findings with evidence references and a prioritised remediation roadmap.
06
Follow up
Re-test remediated items and sustain assurance through continuous monitoring.
Two kinds of assurance — both matter
Periodic and continuous, working together.
Periodic Assurance
- Defined scope
- Defined period
- Evidence selected and tested
- Independent assessment / audit where applicable
Continuous Assurance
- Ongoing visibility
- Control health
- Evidence freshness
- Risk movement & control changes
- Exceptions & remediation status
- Current governance posture
Continuous assurance complements periodic audit and assessment — it does not replace them. Explore Continuous GRC Assurance →
Framework & regulatory alignment
We assess against the standards your stakeholders recognise.
Framework names describe the audit criteria we assess against and do not imply accredited certification authority.
Evidence-based deliverables
What clients receive.
Every engagement is scoped individually — we only promise deliverables appropriate to the service and scope.
Industries we serve
Product-accelerated assurance
Our technology products make assessments faster and evidence fresher.
Frequently asked questions